Malicious Airdrop App Slips Into Official Crypto Store, Targets Wallet Recovery Phrases
TL;DR:
- Cybersecurity researchers identified a fraudulent app simulating token airdrop distributions within an official application catalog.
- The malicious software required the manual entry of 12- or 24-word seed phrases as a mandatory requirement to process alleged reward claims.
- Technical reports confirmed that the cryptographic credentials were transmitted directly to remote servers controlled by the attackers.
Another security breach was reported this Monday, November 2, when a malicious airdrop app infiltrated an official software repository, deploying a structured mechanism to siphon cryptocurrency wallet recovery phrases. The incident, reported by digital forensics firms, triggered technical alarms across multiple platforms after the direct exposure of affected users’ digital assets was confirmed.
Today a malicious third party app named “SKR Claim” was submitted to the Solana dApp Store. The App Spotlight and Quests UI were updated following unauthorized access to the dApp Publishing Portal. The app requested entry of user seed phrases.
The app was live on the dApp…
— Seeker | Solana Mobile (@solanamobile) November 1, 2026
The fraudulent tool adopted a visual identity that mimicked established brands within the decentralized ecosystem. Preliminary code analysis revealed that the program operated without executing any real interactions with blockchain networks during transaction processing.
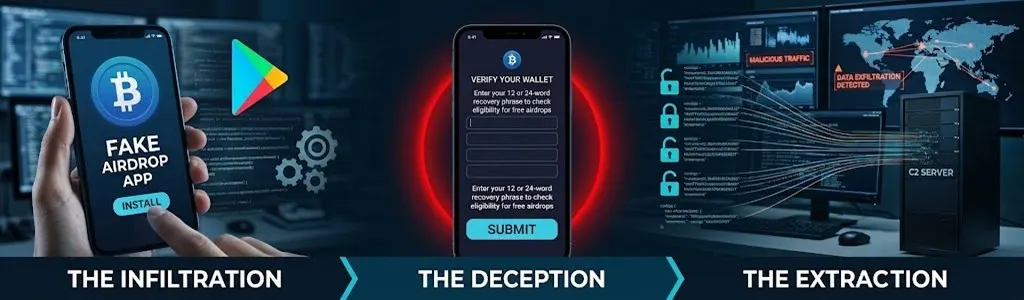
The attack vector relied exclusively on digital persuasion. Once installed on the victim’s device, the application prompted the synchronization of the primary wallet under the pretext of verifying eligibility for free asset distributions.
Extraction Mechanism and Identity Impersonation
The software’s operational flow included forms designed to capture 12- and 24-word mnemonic phrases. The investigation report indicates that the system blocked any progress within the interface until the victim entered the complete sequence into the corresponding fields.
In the lab, tests showed that entered data was neither validated locally on the client side nor routed to decentralized nodes. According to documented network traffic logs, the confidential information was encapsulated and forwarded via encrypted requests to an external command-and-control server.
According to analysts, the hackers bypassed the store’s review filters using a technique known as deferred payload delivery. This strategy involves submitting a basic build that complies with initial security policies, only to later enable hostile features through remote updates.
Figures disclosed by researchers indicate that the app amassed thousands of downloads before community reports facilitated its formal detection. Case documentation shows that the attackers targeted both self-custody browser extension wallets and mobile storage solutions.
Web infrastructure security specialists identified that the domain associated with the receiving server used SSL certificates issued just days before the campaign launched. Domain registration records displayed anonymous registration patterns intended to obstruct the geographic identification of the system operators.
The cybersecurity firms involved in the case submitted the corresponding notification to the app store administrators. Official documentation confirms that the malicious package identifier was removed from the public catalog following verification of its hostile behavior.
This story was originally published by Crypto Economy. Read the original article.