Coinbase Launches New Security Checks to Protect Crypto Transfers
TL;DR:
- Date and series: Coinbase published on November 19, 2026, the first installment of its 10-article technical series titled Coinbase Security Proof of Work, focused on transaction intent verification.
- Three technical improvements: The update adds a proprietary cryptographic signature to user approval, expands checks through the signing stage, and extends control to more transfers with default halting if verification fails.
- Audited parameters: Before signing a transaction, the system checks that the asset, amount, and destination address match what the client approved.
Coinbase will execute new security checks in the cryptocurrency transfer flow as the opening of its Coinbase Security Proof of Work series. The measure operates in the background without requiring extra settings from users when sending funds from the platform.
The exchange reported that a valid cryptographic signature with the private key demonstrates authorization before the blockchain network, but does not by itself validate whether the transaction matches what the user wished to send. The post notes that networks accept validly signed transfers without verifying correspondence with the client’s original intent.
Intent Verification Architecture in Transfers
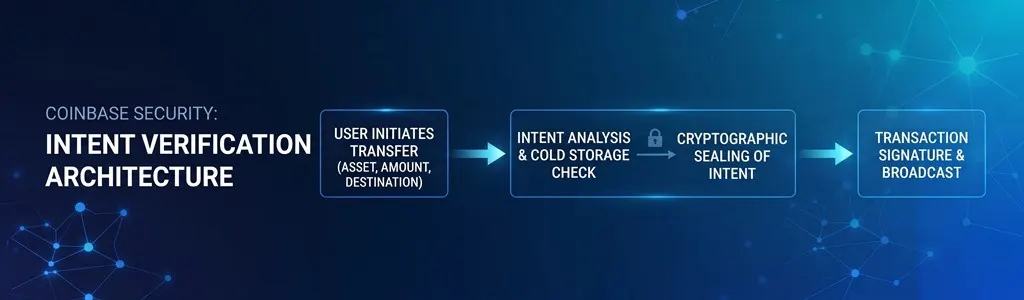
Data published by Coinbase on November 19 reveal that intent verification already existed in its infrastructure and recorded user approval in a separate service to cross-check it at the start of the process. Now the company strengthens that mechanism through three concrete technical changes.
The first change consists of sealing user approval with a proprietary cryptographic signature. According to Coinbase, this sealing gives its systems a deterministic way to verify that the transfer matches exactly what was approved.
The second adjustment extends checks to more stages of the operational flow, reaching the signing phase. The third component expands control to a higher volume of transfers and halts by default operations that fail verification.
Information disclosed by Coinbase indicates these checks act on the asset, amount, and destination before signing the transaction. If any of those fields does not match what was recorded in the approval, the system blocks the send.
Technical Limits Against Deception and Complementary Controls
Coinbase‘s technical report specifies that intent verification confirms consistency between what was approved and what was executed, but does not detect whether the user was deceived into approving a harmful transaction. The company explains that if a scammer convinces someone to send funds to their address, the approval still belongs to the account holder.
For that reason, it recommends manually reviewing four details before confirming any send: the asset or token, the exact amount, the full destination address —including the middle section against address-poisoning attacks— and the selected blockchain network. The official text warns that sending funds over an incorrect network can prevent recovery.
The company also reminds users they can enable address allowlisting to restrict sends solely to previously approved destinations. Likewise, the post underscores that Coinbase does not ask to move funds to keep them safe and advises turning to in-app support when facing urgent messages via phone, text, email, or social media.
In the broader context of its custody architecture, Coinbase reported on November 4, 2026, that it holds more than 99% of client assets in cold storage. The document from that date adds that transfers feature distributed keys, withdrawal limits, anomaly detection, and circuit-breaker mechanisms capable of halting signing.
This Thursday’s post forms part of a ten-part editorial series announced by Coinbase on hardening its security stack. Subsequent chapters of Coinbase Security Proof of Work will progressively detail the exchange’s other technical protection layers.
This story was originally published by Crypto Economy. Read the original article.