Binance Hack: Fake Interviews and Months of Hidden Access
TL;DR:
- Two Binance engineers suffered independent security breaches between June and September via malicious software and a fraudulent hiring process.
- Attackers drained approximately $6.3 billion on October 29, of which the company claims to have frozen nearly $2.85 billion.
- The FBI officially attributed the breach to the North Korean group TraderTraitor following months of covert access to internal infrastructure.
Thursday, October 29, 2026, is marked on the calendar as the day Binance was hacked. Today, it is known that the incident originated from the prior compromise of two corporate engineers through bogus job interviews and malicious software.
— Binance (@binance) November 3, 2026
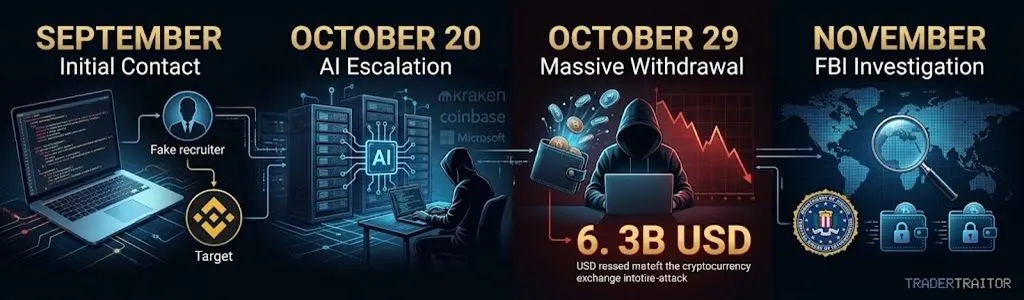
The official report reveals that the first breach occurred in June, when an employee downloaded a compromised package while researching AI tools. The company detected this initial infection at the time, proceeded to physically replace the machine, and reset the associated corporate credentials.
However, the data gathered by the hackers during that initial window enabled them to map the organizational structure and pinpoint the members of the technical wallet department.
In September, the second phase of the infiltration was carried out. That month, purported recruiters contacted another exchange engineer through a legitimate job platform. The interactions took place via video calls with supposed human resources staff and an individual impersonating the chief executive officer.
During that technical evaluation, the candidate received a coding test with attachments containing malicious code designed to bypass device security controls.
Data released by Binance indicates that around October 20, the operators behind the intrusion used the compromised workstation and an internal AI tool to reach out to other engineers on the team.
Through this lateral privilege escalation, the perpetrators obtained deployment credentials, which they subsequently used to inject unauthorized software into the exchange’s wallet infrastructure.
Infiltration Methods and Industry Precedents
Unauthorized withdrawal operations took place on October 29, totaling approximately $6.3 billion transferred out of the platform’s reserves within hours.
Binance representatives stated that they managed to freeze roughly $2.85 billion in assets linked to the attack and that 98% of the affected balances were restored using the company’s own treasury funds.
The FBI formally attributed the incident to the North Korean threat group TraderTraitor, an organization known for orchestrating campaigns aimed at digital asset firms.
Industry specialists note that infrastructure firms and trading platforms had recently reported identical attack vectors.
In May 2025, executives at the Kraken exchange reported intercepting an operation tied to North Korea that attempted to apply for roles on their technical development team.
Similarly, Coinbase issued an internal alert in August 2026 after identifying irregular activity linked to a contractor with compromised access privileges.
Microsoft had also issued formal warnings in March detailing how state-sponsored groups were leveraging fake coding assessments during recruitment interviews to compromise developer endpoints.
The chronological account provided by Binance, complete with specific dates and events, leaves lingering technical questions regarding the lack of network segmentation that permitted unverified code execution on workstations tied to its production environment.
Furthermore, the post-incident audit is reviewing how the initial June compromise retained operational value for the threat actors and how deployment keys were able to authorize massive capital outflows without secondary containment checks.
Forensic investigation teams and regulatory agencies continue their efforts to trace the receiving wallets holding the remaining funds over the coming weeks.
This story was originally published by Crypto Economy. Read the original article.